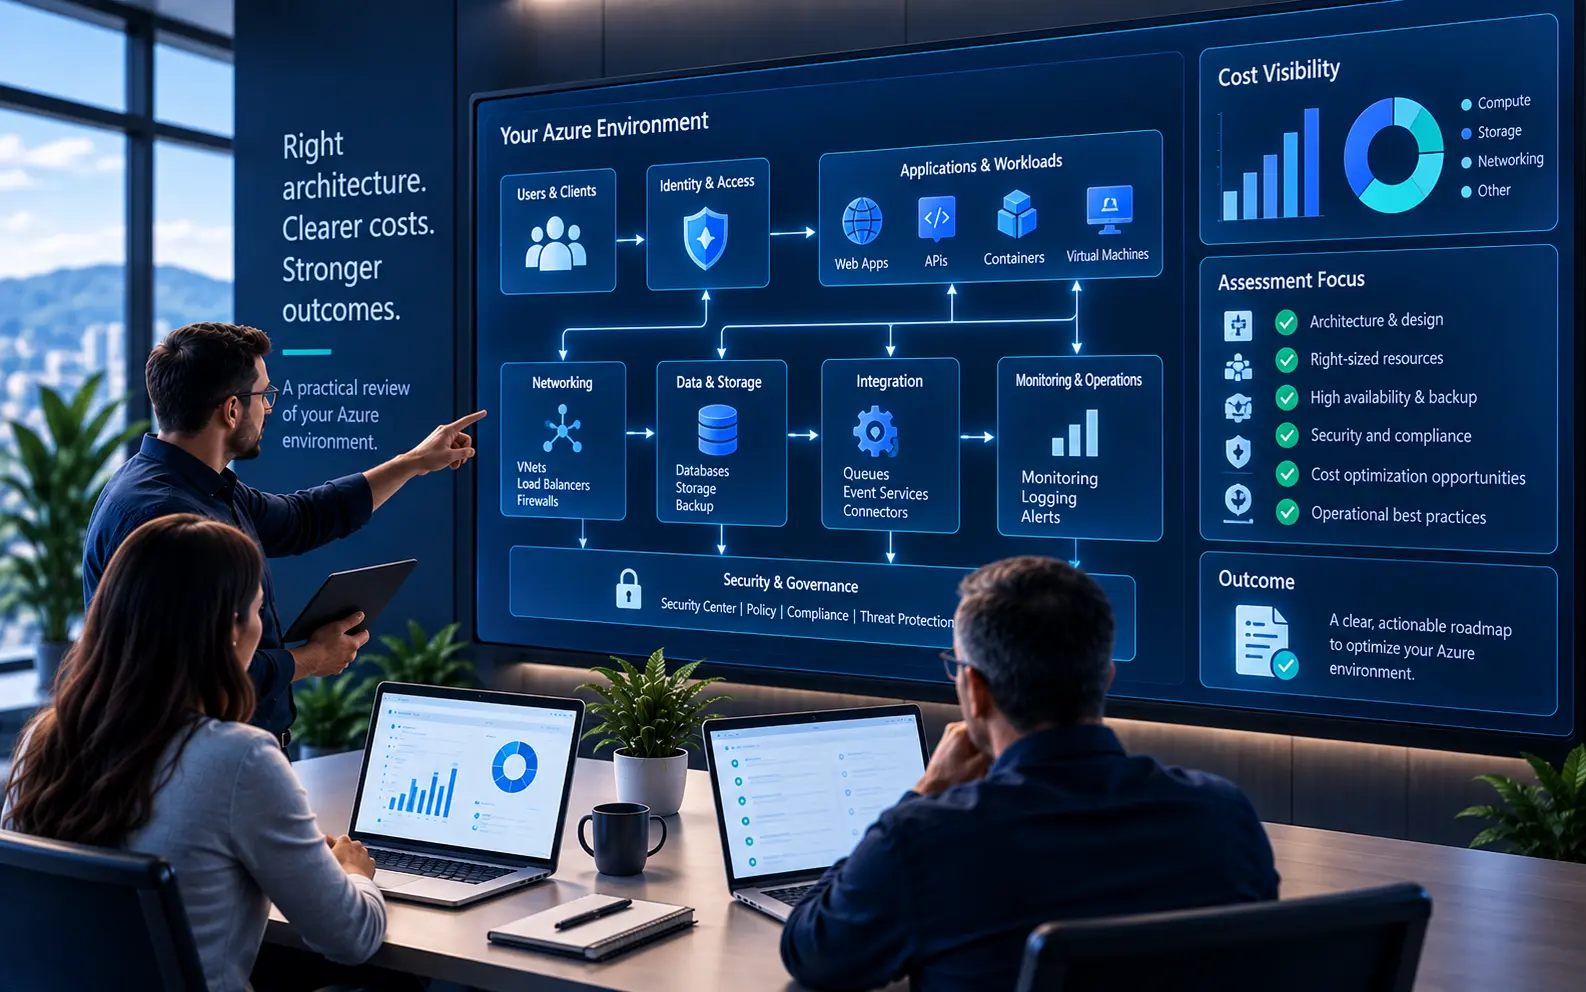
Azure environments tend to grow faster than the documentation about them. A subscription created for a pilot becomes production. A virtual machine sized for a migration weekend is still running at that size two years later. Networking is extended one project at a time. None of this is unusual, and none of it is a reason to start changing things before the environment is understood.
Inventory what is actually there
The first step is a plain inventory: subscriptions, resource groups, workloads, and the resources behind them. For each workload, it should be possible to answer what it does, who depends on it, and who is responsible for it. Resources that cannot be tied to a workload or an owner are the ones most likely to be forgotten — and most likely to be costing money or carrying risk.
Consistent tagging makes this much easier to maintain. Owner, application, environment, and cost center are a reasonable starting set, as long as someone keeps them accurate.
Follow the dependencies
Workloads rarely stand alone. An application may depend on a database in another resource group, a storage account shared with three other systems, a VPN back to an office, and an identity configuration in Entra. Changing one piece without understanding those dependencies is how routine maintenance turns into an outage.
Mapping dependencies does not require an elaborate diagram. It requires knowing which pieces talk to which, and which of those connections would break if something moved.
Read the bill as a map
Azure Cost Management shows where money is going, and that is often the fastest way to see how the environment is really used. Large line items point to important workloads. Steady spending on resources nobody recognizes points to cleanup opportunities. Idle or oversized compute, unattached disks, and old snapshots are common findings.
Commitment options like reservations and savings plans can reduce cost for stable workloads, but they make most sense after right-sizing — not before.
Check the operating basics
Before any larger change, confirm the fundamentals: who has administrative access and why, whether backups exist and have been restored successfully, what monitoring and alerting is in place, and how changes are made and recorded. Azure Advisor recommendations are a useful input, but they are recommendations to evaluate, not a to-do list.
Once the environment is understood, decisions about modernization, migration, or consolidation become much clearer — and much safer.